StackOne Single Sign-On (SSO) lets the organization’s users sign in through its own SAML 2.0 identity provider (IdP). StackOne acts as the SAML service provider (SP), and the IdP authenticates users. Each organization has one SSO connection, bound to one email domain. Once that domain is verified, anyone whose work email is on it signs in through the IdP instead of with a StackOne password. They can start from the StackOne sign-in page by entering their email, or open the StackOne app from the IdP.
Signing in with SSO doesn’t add anyone to the organization. To add users, see Manage Team.

Set up an SSO connection

The guide for your SAML IdP takes you through each part of the setup:
  • Creating the SAML app in the IdP.
  • Registering it in StackOne.
  • Verifying the domain.
  • Managing the connection afterward.

Okta

Microsoft Entra ID

Other SAML 2.0 provider

Require SSO

Once the domain is verified, you can require users to sign in through SSO and turn off email and password sign-in.
Enforcing doesn’t check that sign-in works. A misconfigured SAML app, an unassigned user, or a certificate or issuer mismatch still enforces, and anyone the IdP can’t authenticate is locked out. Before you enforce, open a private or incognito window and complete an SSO sign-in as a user assigned to the app in the IdP, not only your own account.
  1. Go to Organization > Security > Authentication.
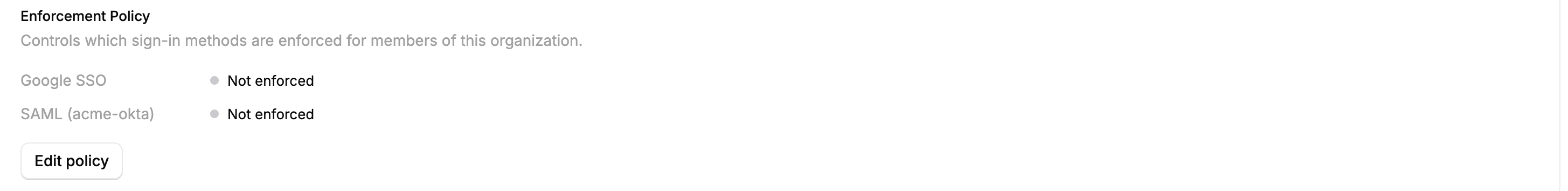
  2. On the Enforcement Policy card, select Edit policy.
  3. Add the SAML connection to Enforced methods.
  4. Select Save changes.
The Enforcement Policy panel under Organization > Security > Authentication, where you add the SSO connection to the enforced sign-in methods.
Enforcement takes effect as soon as you save. Anyone whose session didn’t come through an enforced method, including you, is asked to sign in through the IdP the next time they load a page or switch to the organization.
Locked out after enforcing? An Organization Admin who can still reach the dashboard can remove the method from the Enforcement Policy to restore password sign-in. If no one can get in, contact StackOne support.

Next steps

Just-in-Time Provisioning

Add users who aren’t members yet when they sign in, and map an attribute to organization admin.

SCIM Provisioning

Provision and deactivate members automatically from the IdP.

Groups

Grant many members the same project or account access at once.